Microsoft says a hacking group used the AI tool ARTEX against hundreds of organizations
On 21 October 2026, Microsoft said a China-state aligned group it calls Storm-0940 used ARTEX, an open-source AI penetration testing tool, to automate attacks on hundreds of organizations since as early as September. In several cases it took under 3 hours to reach privileged cloud access. Microsoft links the group to the ConnectWise supply chain compromise.
The short version
- 01Microsoft says Storm-0940 used the agentic AI tool ARTEX to automate attacks on hundreds of organizations.
- 02In several cases, the time from first targeting to privileged cloud access was under 3 hours.
- 03ARTEX is open source and can use any AI model.
- 04Microsoft assesses the same group was behind the ConnectWise supply chain compromise.
- 05Microsoft says the activity did not come from a flaw in its own products.
At a glance
| Published | 21 October 2026 |
|---|---|
| By | Microsoft Security |
| Group | Storm-0940, China-state aligned, active since 2021 |
| Tool | ARTEX, an open-source AI penetration testing framework |
| Scale | Hundreds of organizations, as early as September 2026 |
| Speed | Under 3 hours to privileged access in several cases |
| Status | Confirmed |
What did Microsoft say happened?
Microsoft's security team says a group it tracks as Storm-0940 used the agentic AI penetration testing framework ARTEX to automate attacks, as early as September 2026, on hundreds of organizations around the world. The targets span industries such as aerospace and defense, energy, financial services, government, legal and software, according to Microsoft's blog post.
Microsoft describes Storm-0940 as a China-state aligned actor that has been active since 2021.
What is ARTEX?
Microsoft says ARTEX is an open-source penetration testing framework that can use any AI model. It is a system of AI agents that can run an autonomous security test, from scouting through to data theft, with little human help. Its agents build a graph of the assets and weaknesses they find.
Penetration testing means trying to break into a system on purpose to find its weak spots. Microsoft says Storm-0940 used the tool to speed up scanning, password guessing and the abuse of app permissions.
How fast and how big was the campaign?
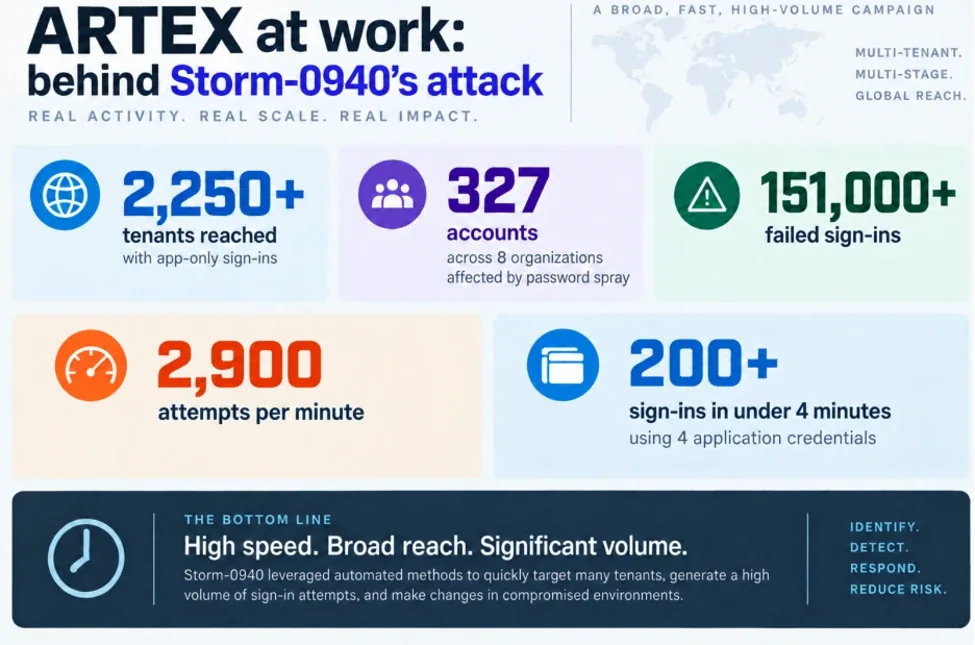
Microsoft says that in several cases the time from first targeting to privileged access to an organization's cloud was under 3 hours. It says the speed leaves defenders very little time to respond.
Its own chart counts more than 2,250 cloud tenants reached with app-only sign-ins, and peaks of 2,900 sign-in attempts per minute. In one password-guessing run from 10 to 14 October, it saw 327 accounts targeted across eight organizations and more than 151,000 failed sign-ins. It says it saw no successful sign-in from that run.
How does it connect to ConnectWise?
Microsoft says it assesses that Storm-0940 was responsible for the recently disclosed ConnectWise supply chain compromise of a multi-tenant application. A supply chain compromise means attackers get in through a supplier's software instead of attacking each customer one by one.
ConnectWise published an advisory on 16 October. Microsoft says the group used stolen credentials for ConnectWise cloud applications to sign in to customers' accounts. It also says the activity did not come from a compromise of, or a flaw in, Microsoft's own systems or products.
What does Microsoft tell customers to do?
Microsoft says to keep affected ConnectWise application connections disabled until ConnectWise gives formal restoration instructions. It also says not to delete enterprise applications as the first step, and to save logs and evidence first.
It lists checks for sign-in and audit records from at least 15 October, and detection tools in Microsoft Defender.
Why does it matter?
AI tools that run a whole attack with little human help let attackers move faster. Microsoft says the speed of this activity leaves defenders little time. The same type of tool is also built for security teams to test their own systems, and Microsoft notes this one is open source.
What's next?
Microsoft's advice for now is to keep affected ConnectWise connections off until ConnectWise gives formal restoration instructions. Check ConnectWise's advisory, published 16 October, for the latest steps.
Questions people ask
Who is Storm-0940?
Storm-0940 is Microsoft's name for a China-state aligned group that has been active since 2021 and targets organizations across many industries for data theft.
Is ARTEX illegal?
Microsoft describes ARTEX as an open-source penetration testing framework. Security teams use such tools to test their own systems. Microsoft says Storm-0940 used it for attacks.
Was Microsoft hacked?
Microsoft says the activity did not result from a compromise of, or a flaw in, its own systems or products.
How fast was the attack?
Microsoft says that in several cases it took under 3 hours from first targeting to privileged cloud access.
What should affected ConnectWise customers do?
Microsoft says to keep affected ConnectWise application connections disabled until ConnectWise gives formal restoration instructions, and to preserve logs first.
Sources
- PrimaryMicrosoft Security Blog: AI-driven, large-scale nation-state campaign using ARTEX (21 Oct 2026)
Why "Confirmed"? We label a story "Confirmed" when the company or government announced it itself. Spotted an error? Email hello@openloopnews.com and we will correct it.